

One point of interception
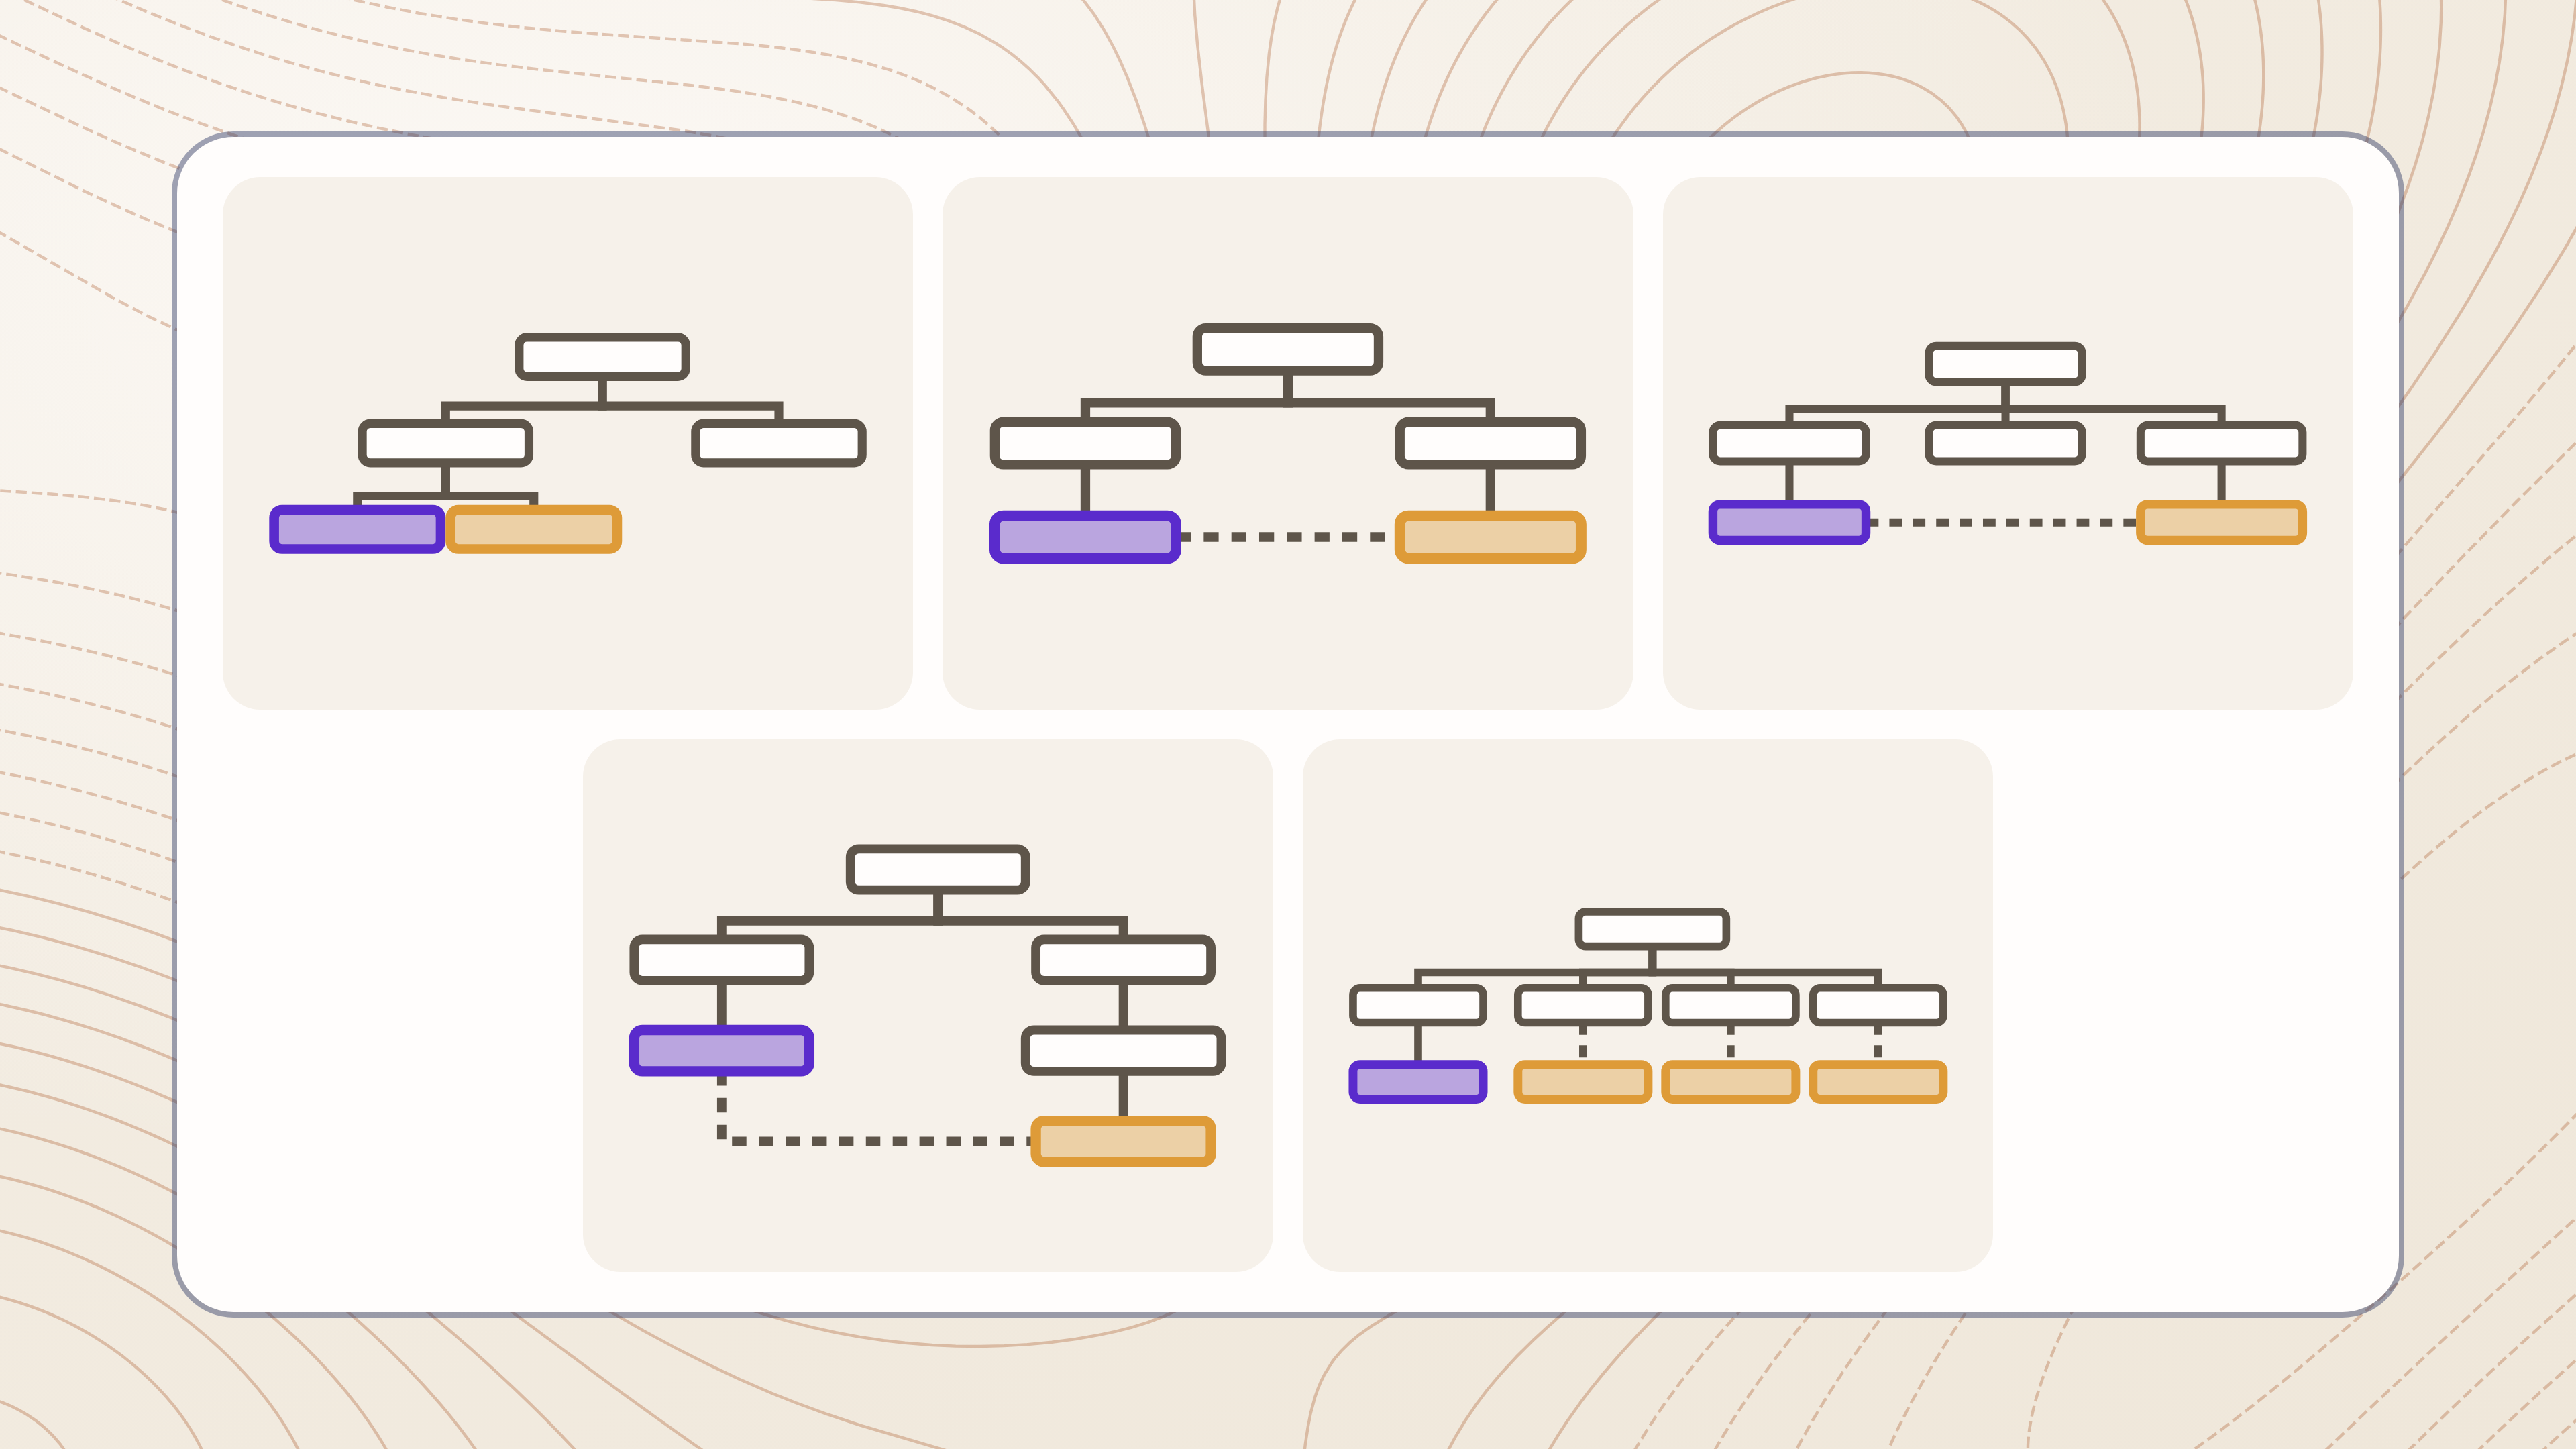
Every agent routes through one checkpoint, and the same component that sees the traffic decides what happens to it. It sees what crosses that boundary, applied the same way to every agent behind it.
Most products advertising as agent security watch agents from one
surface or one stream of traffic.
Geordie understands each agent
from the harness it runs in, across cloud, code, endpoint and browser,
so you can accelerate agentic operations safely.




And dozens more
A gateway sees the requests and tool calls that pass through it, which makes it a useful checkpoint, but an agent’s skills, memory and local tools sit in its own configuration and never cross that path.
Every agent routes through one checkpoint, and the same component that sees the traffic decides what happens to it. It sees what crosses that boundary, applied the same way to every agent behind it.
Geordie reads each agent from its configuration, context and behavior across every stage of its work and every surface it runs on.
Attaches at every step of the loop
01
Which agent, which harness, who asked, and what for.
02
Configuration, loaded context, skills present, memory carried over.
03
The plan, while guidance is still free to give.
04
Every tool type: skills, extensions, plugins, packages, connectors, direct API.
05
The decision, in the context of the whole session.
06
The outcome, the owner, the tokens, immutably recorded.
The advantage comes from position rather than effort. A tool that sits outside the agent can’t read the agent’s memory however good its detection is, and a tool that reads the agent’s memory doesn’t need to guess.
Agent controls added to a much larger existing suite. Enormous distribution, low procurement friction, and agent governance as a line item rather than the core bet.
Built for agents, but one component both intercepts and enforces, so coverage ends where routing does, and pausing enforcement to troubleshoot also cuts visibility.
Close to agents that run where a person sits, but most see an agent only once it runs on a monitored device, and coverage stops short of cloud, code and multi-agent work.
Geordie reads each agent where it runs, through a sensor on the endpoint, cloud and SaaS APIs, a connection to code repositories and a browser extension - and then it controls risks through the agent’s own configuration
claims-triage
Owner: R. Hernandez



 Policy admin Approved Payments Approved Unapproved server High
Payment instruction issued without a policy match
Payment instruction held until a policy match is confirmed
11% on retried tool calls
Allow or block is the only vocabulary available to something sitting outside the agent. From inside, responses are context-specific and escalate with risk, from observation to binding, and every one is deterministic.
Beam watches the action and writes it to the immutable record without touching it. The agent proceeds exactly as it would have, and the team gets the evidence it needs to decide whether anything stronger is warranted.
Beam writes additional context into the agent’s reasoning and offers an approved pathway. Nothing is blocked; an agent heading somewhere it is not authorized for is guided to an equivalent it is, and the work continues.
A new mode for the Claude ecosystem. The agent stops and waits for an explicit decision to continue or not. Beam delivers the context behind the pause to the agent, so whichever way the operator decides, the agent carries that context into what it does next.
Lifecycle hooks are binding. Prohibited actions and tool use do not execute, and the attempt is written to the immutable record.
Geordie’s visibility and Beam’s enforcement are independent layers, so coverage can grow across cloud, code, endpoint and browser without changing how controls are applied. Because enforcement runs through the agent’s own configuration rather than an external chokepoint, it adds no latency to governed actions and leaves no single point that can fail open or fail closed.
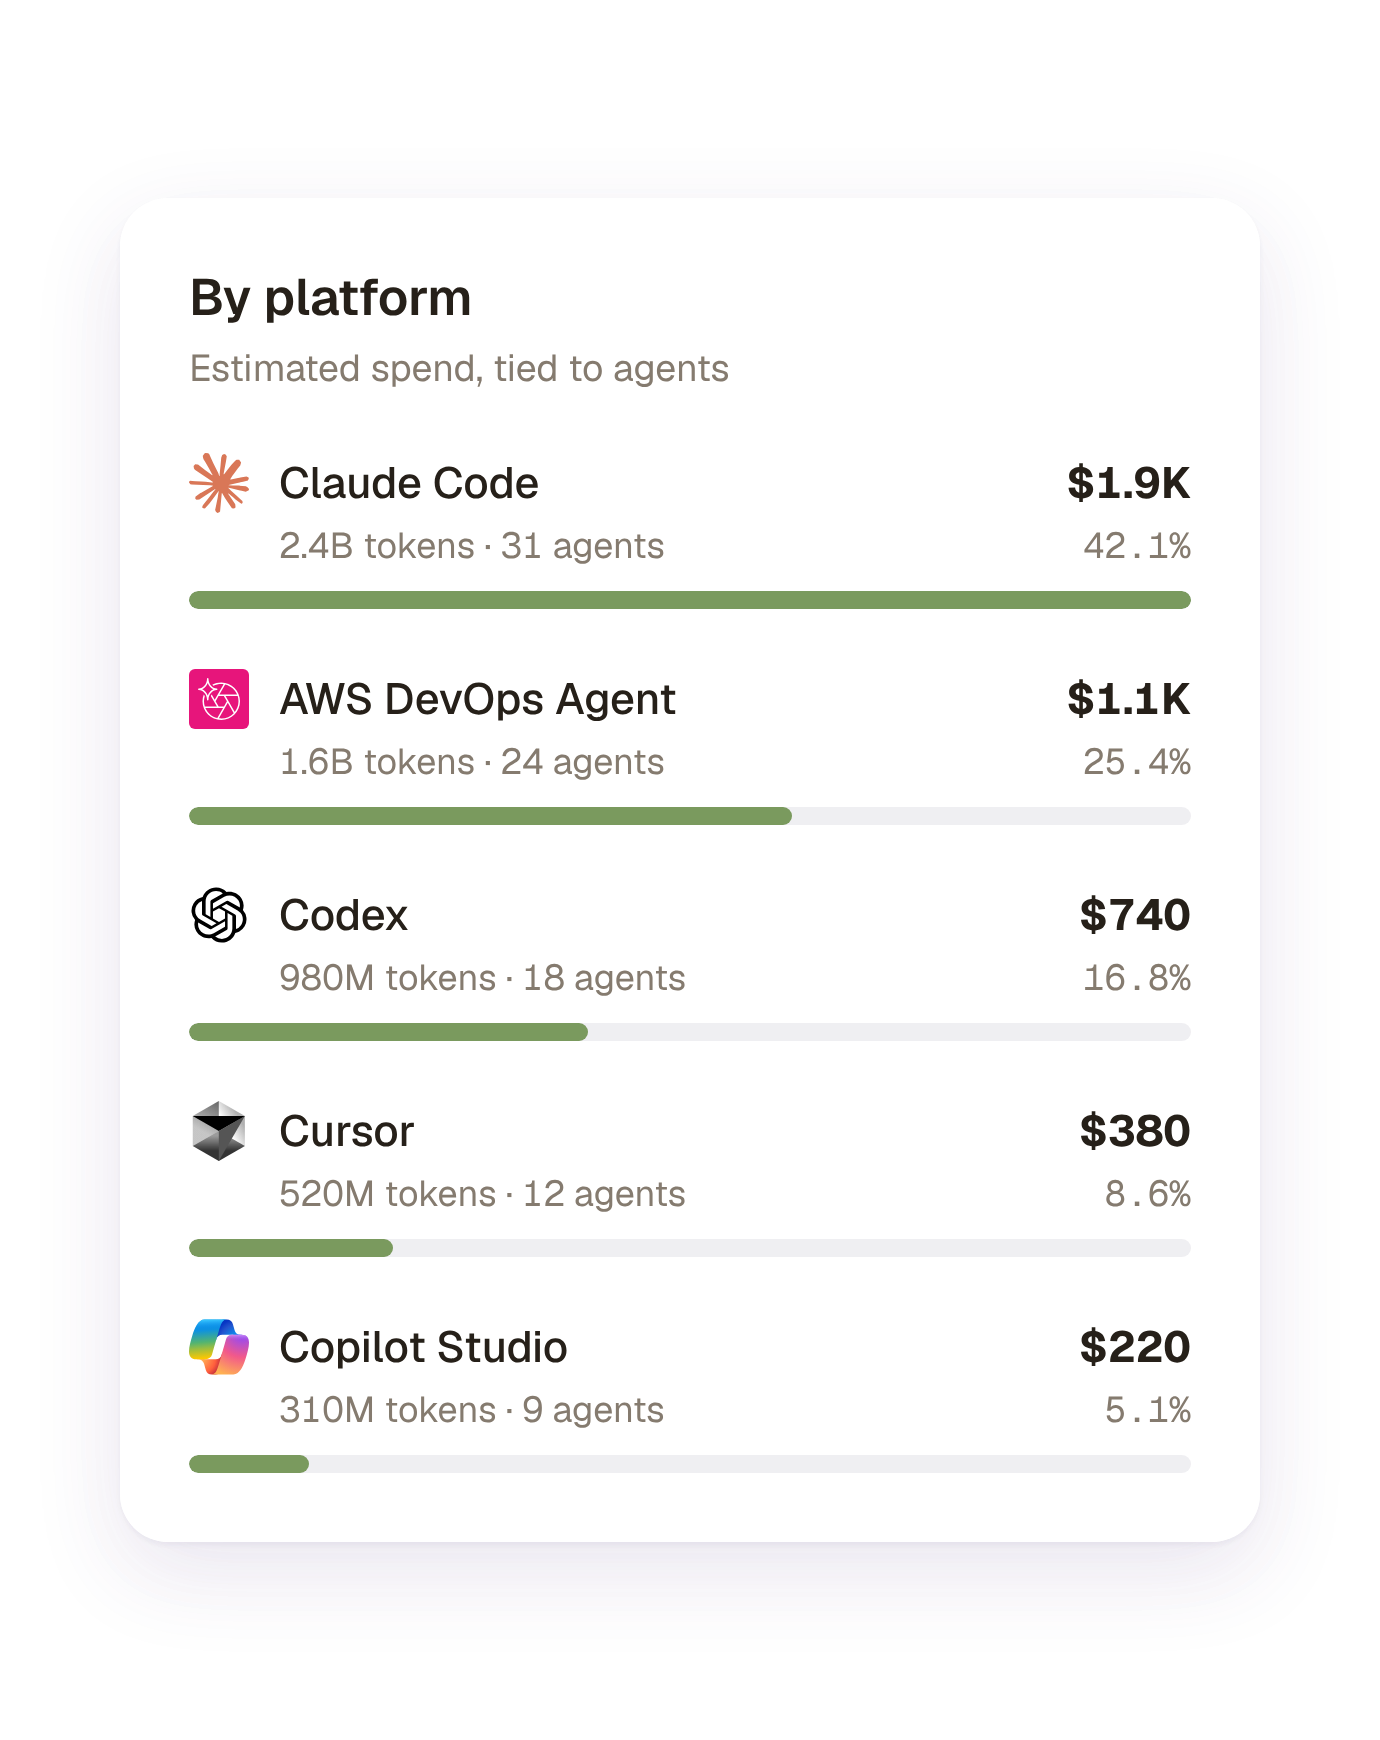
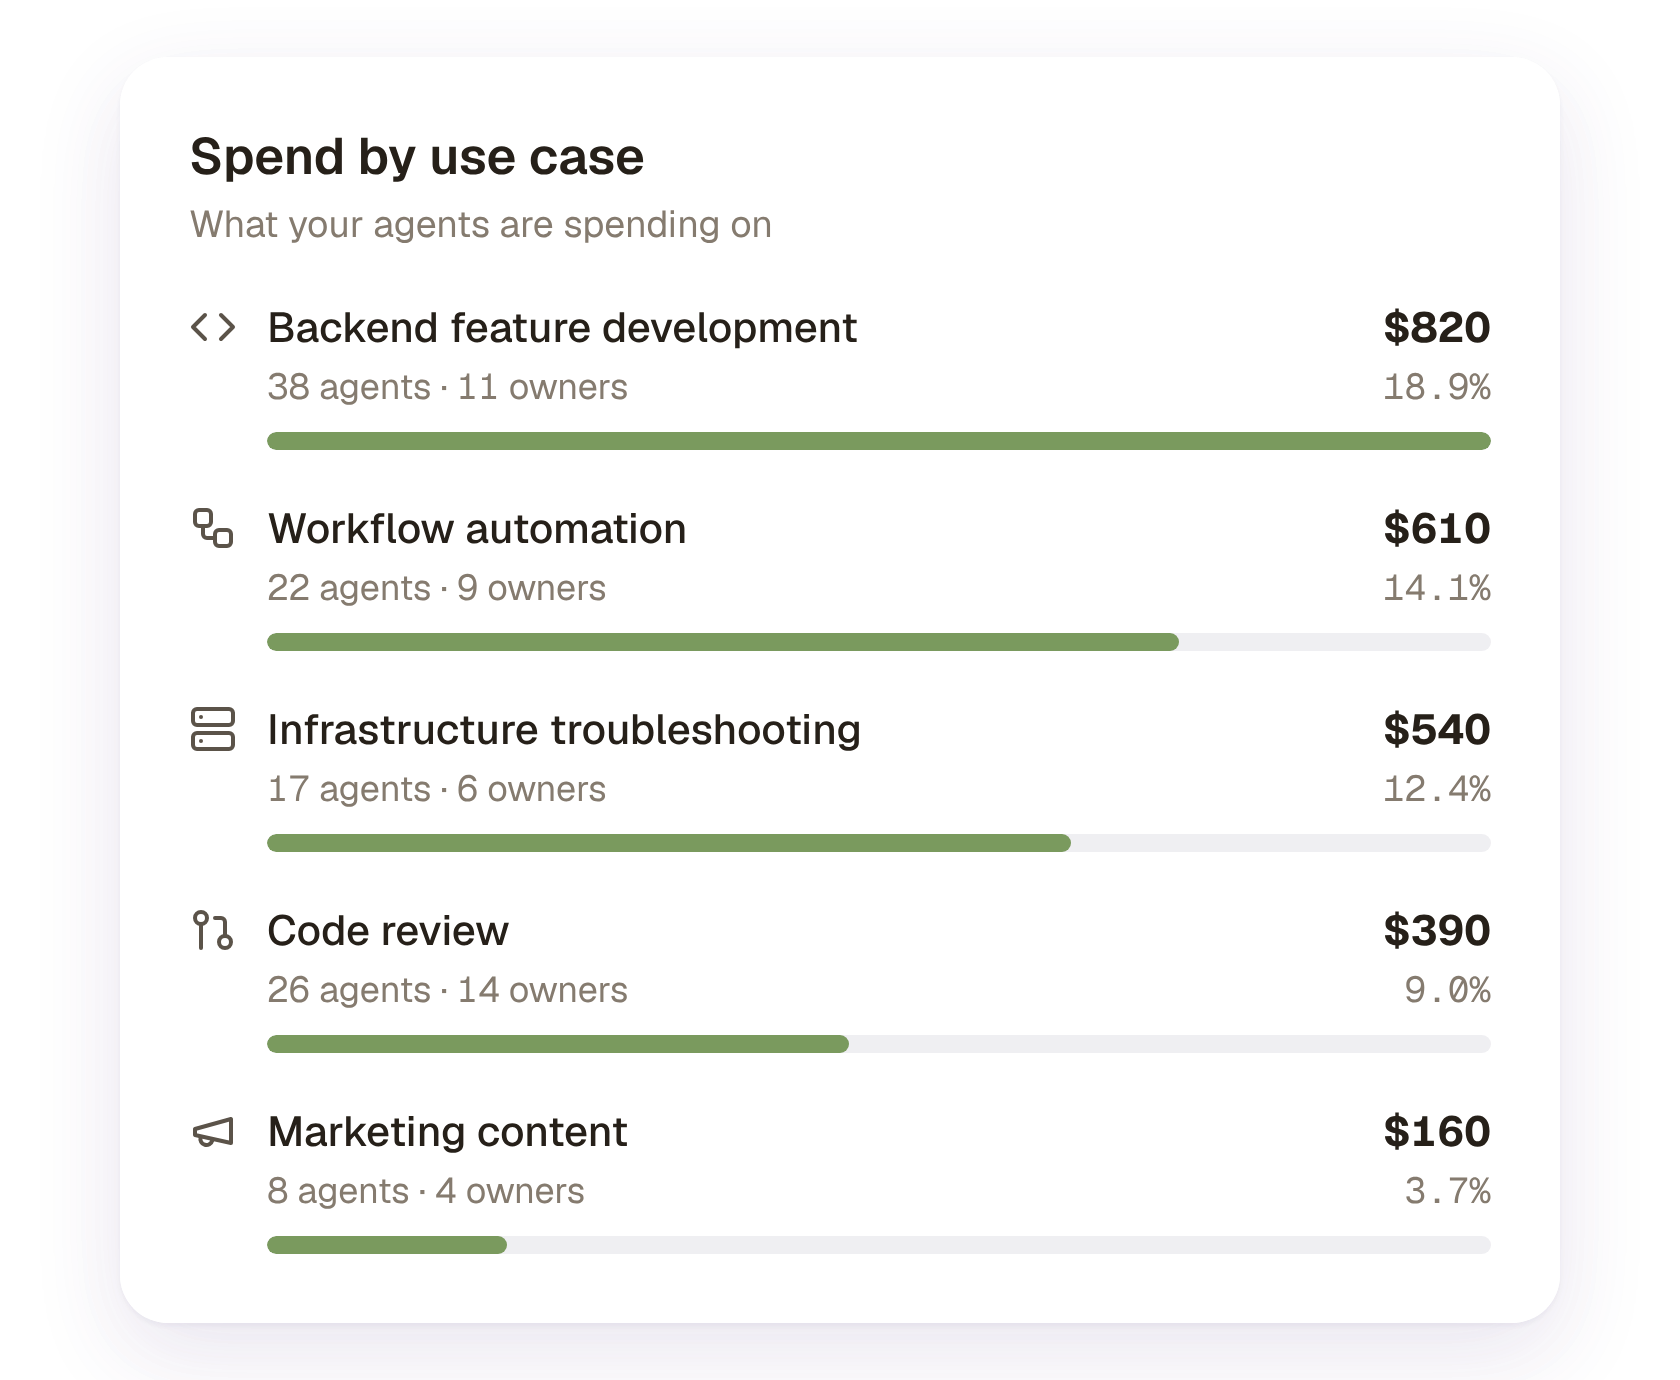
Security asks how much an agent should be allowed to act. The business asks whether agents are acting well and how much they’re costing. Geordie answers both from the same evidence of what each agent actually did, so the record behind a security finding is the same record behind its value intelligence.
327%
more agents than the security team expected, in a single proof of concept, with no reconfiguration required to onboard.
100k+
agents a day under inline control at a US financial data company, with no operational downtime.
~$13M
in exposure avoided, after uncovering three critical CVEs the existing stack had missed.
“My leadership team approved these tools because I could show them what the agents were doing. Not what the model was doing. Not what the network was logging. What the agent was actually doing, step by step, on their behalf.”
“Geordie’s approach gave us visibility close to where agent activity happens, without forcing us into a more complex gateway-based model. It gave us the balance of visibility, governance and architectural simplicity.”
Understand, secure and control your agents, and accelerate your agentic adoption.
Discover your agents across 45+ platforms as well as custom coding agents


Your request has been received.